Secure the AI your business already runs on
Your people use AI every day: copilots, chat assistants, agents and automations. ACE-NSI Cybersecurity gives you the visibility to see it, the governance to shape it and the controls to keep sensitive data where it belongs.
AI is no longer optional. Securing it shouldn't be either.
The question has moved on from whether to adopt AI to how to do it safely, while attackers use the same technology against you.
Adopt AI safely
Enable productivity without losing control of your data, your obligations or your reputation.
- Discover and assess every AI tool, agent and integration
- Classify data and set boundaries before rollout
- Publish a clear, enforceable AI acceptable-use policy
- Map controls to ISO/IEC 42001 and the EU AI Act
Defend against AI-powered threats
Attackers now use AI to scale phishing, impersonation and reconnaissance. Your defences need to keep pace.
- Deepfake and GenAI phishing awareness for your people
- Browser isolation against AI-crafted malicious content
- Deception environments that expose automated attackers
- Continuous, validated vulnerability remediation
Three places we look first
Copilots & productivity AI
Assistants such as Microsoft Copilot inherit every permission a user has. Years of oversharing become instantly searchable. We fix access before you switch it on.
AI agents & automation
Agents, MCP servers and workflow tools like Power Automate, n8n and Make move data and hold credentials. We review what they can reach and what could go wrong.
AI coding & content tools
Coding assistants and content generators can leak source code, secrets and IP. We set guardrails on access, repositories and data so engineers keep their speed.
Assess. Detect. Govern.
A proven sequence that takes you from “we don't know what's in use” to “we can prove it's under control”.
Map the landscape
Inventory AI tools and agents, trace where data flows and score exposure by business impact.
- AI exposure report
- Data-flow map
- Prioritised risk register
Switch on visibility
Deploy monitoring that surfaces new shadow AI and risky prompts continuously, not once a year.
- Continuous discovery
- Real-time alerts
- Monthly insight briefings
Make policy enforceable
Turn principles into policies, and policies into technical controls that apply automatically.
- AI governance framework
- Approved AI register
- Incident playbooks
Every AI tool, agent and connection in one view
Our managed AI visibility service turns raw telemetry into a live registry, risk grades and board-ready insight. Here's what that looks like.
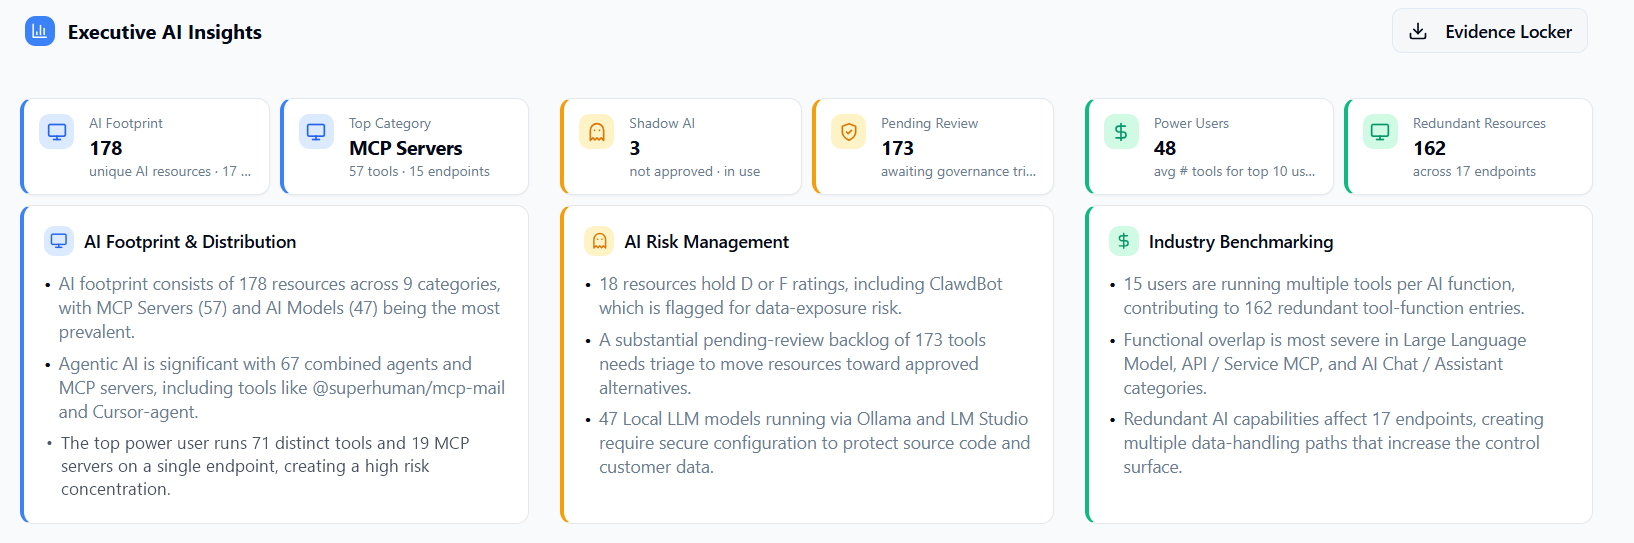
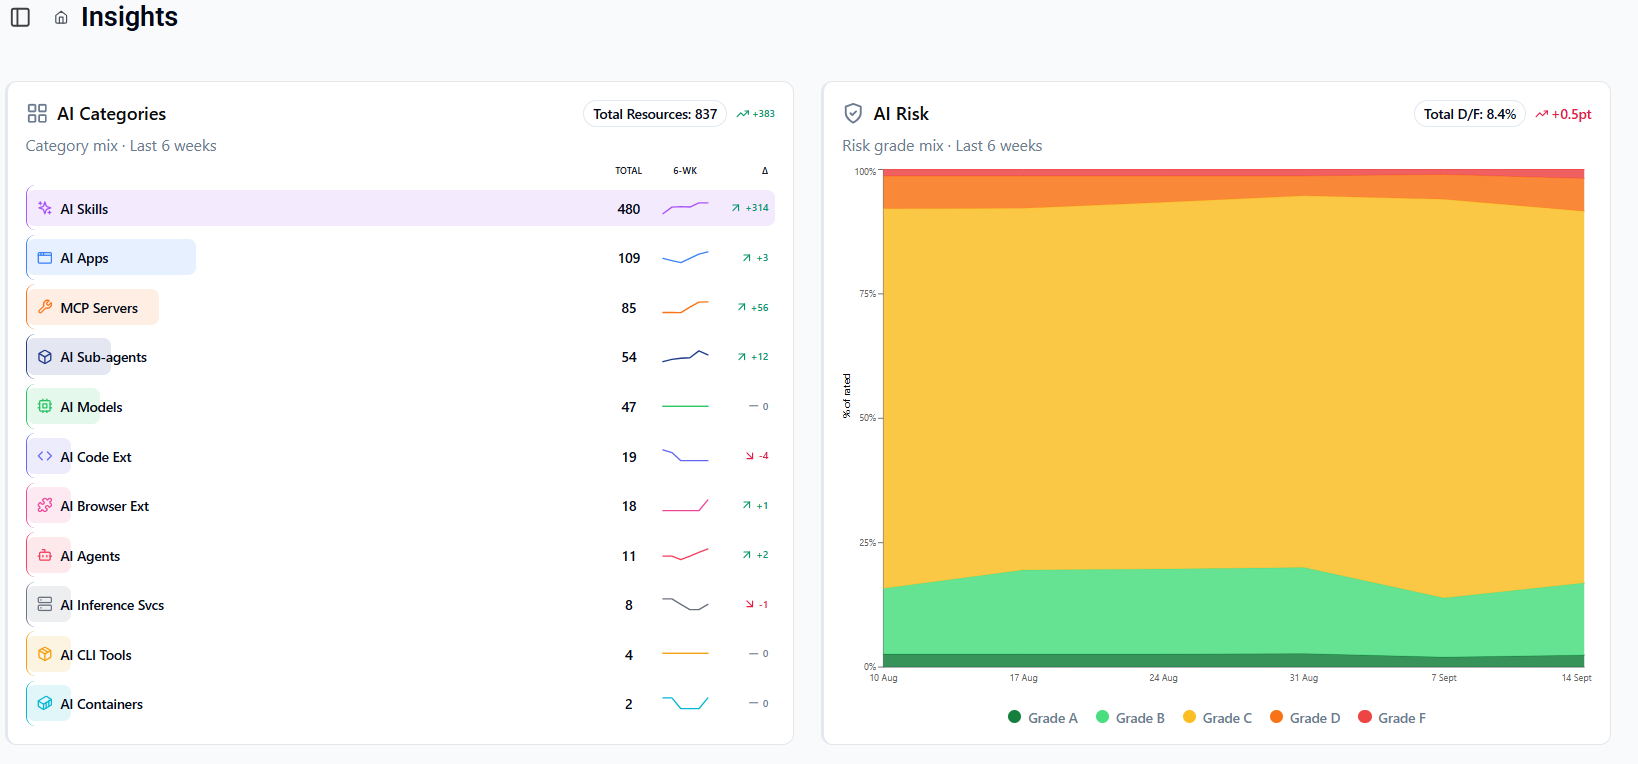
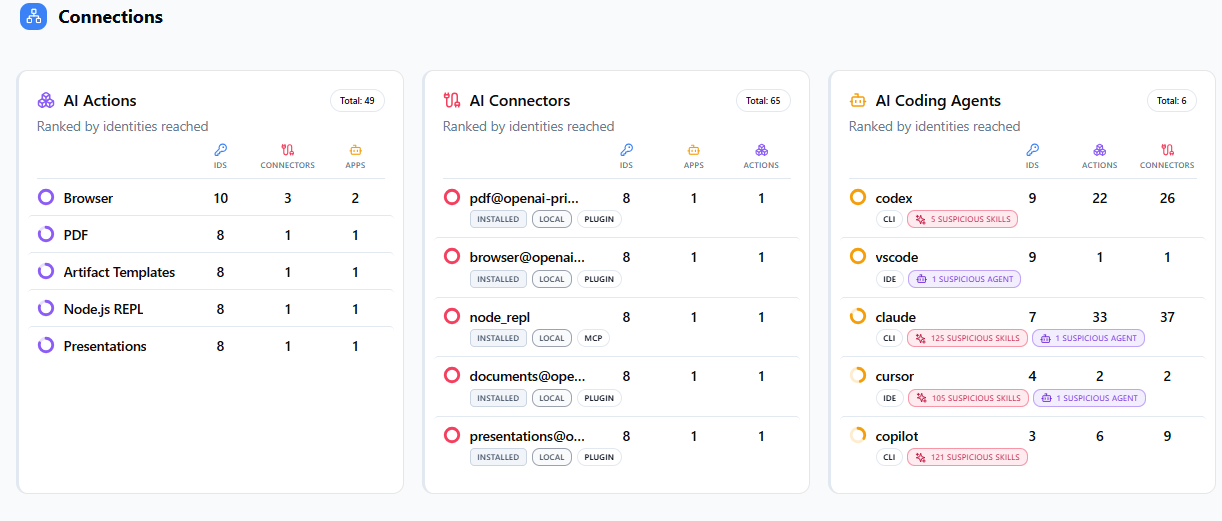
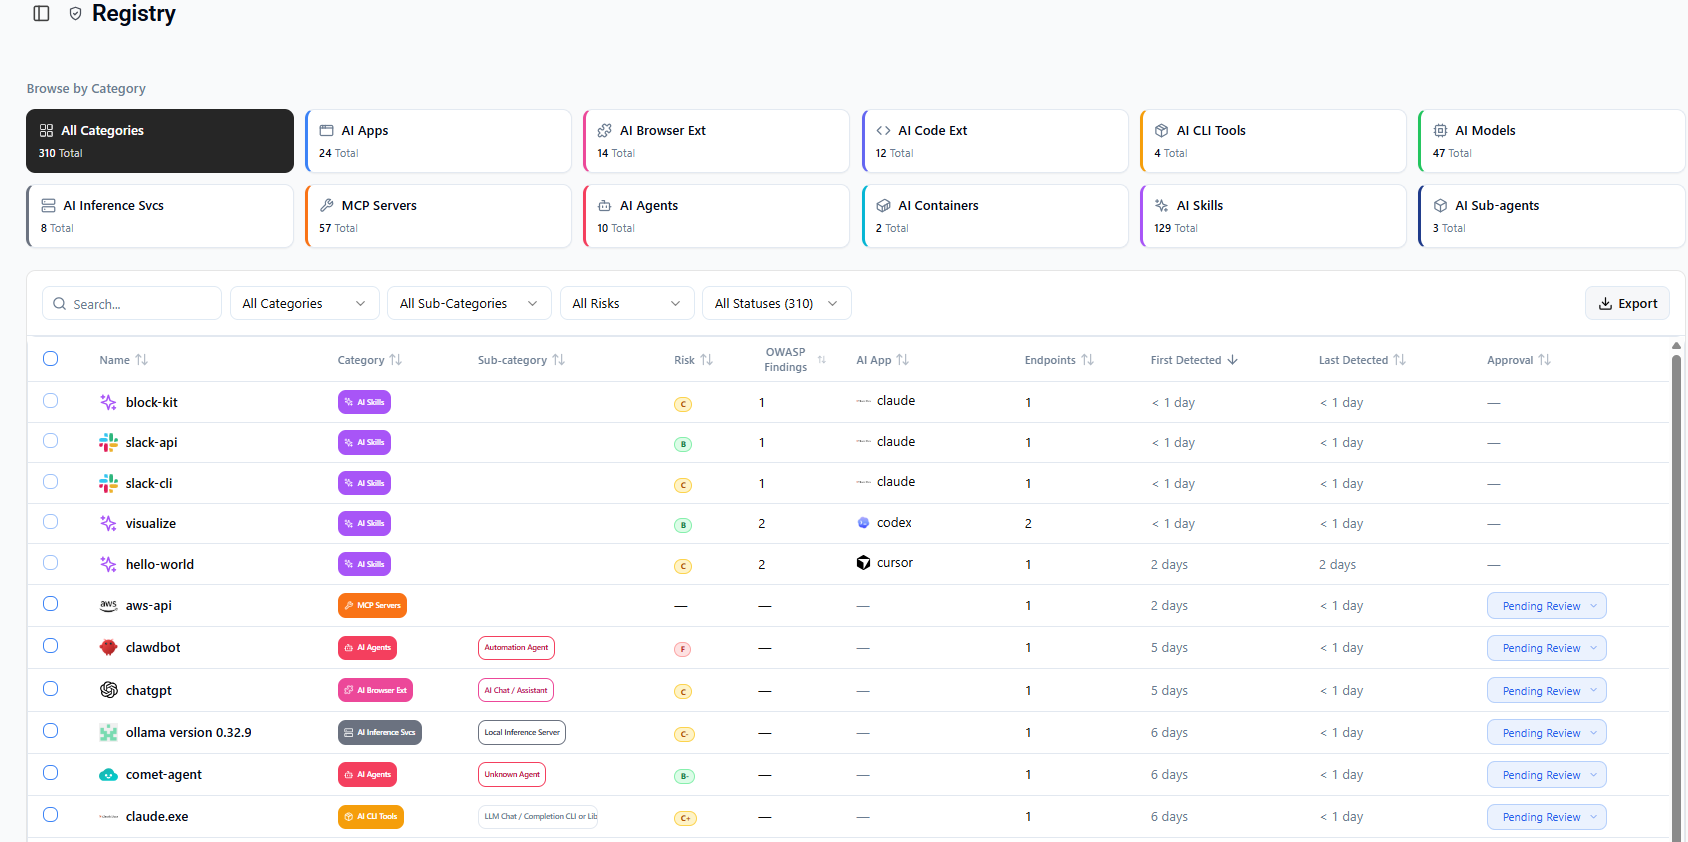
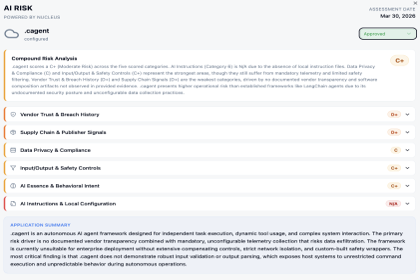
Illustrative data from a demonstration environment.
Real risks, not theoretical ones
These patterns come up again and again in AI assessments. Most organisations have at least one.
Copilot surfaces data users shouldn't see
Salary files, board papers and client records exposed through inherited permissions.
Confidential data pasted into public AI
Contracts, code and personal data shared with free-tier tools on personal accounts.
Unguarded automations holding keys
Workflows with stored credentials and unchecked data paths to third-party services.
Advisory and managed services for every stage of AI maturity
Shadow AI & Exposure Assessment
A fixed-scope engagement that catalogues AI usage, identifies data exposure and delivers a governance roadmap.
AI Governance Framework
Policies, roles, AI inventory and lifecycle controls designed to scale and to prepare you for ISO/IEC 42001 certification.
AI Risk & Impact Assessment
Threat modelling for AI systems covering privacy, model drift, bias, misuse and operational resilience.
Responsible AI & Ethics
Practical principles for fairness, transparency, privacy and accountability, embedded into policy and design rather than left on a slide.
AI Readiness & Secure Deployment
Data classification, sensitivity labels, DLP and permission clean-up, plus architecture review for copilots, agents and workflows.
Managed AI Controls
We deploy and run best-in-class AI security technology for you: discovery, prompt-level data protection and secure browsing.
Aligned to the standards regulators and auditors recognise
We map every recommendation to recognised frameworks so your governance holds up to scrutiny from customers, auditors and regulators alike.
Vet. Isolate. Enable.
Rolling out a new AI capability? Follow the same three steps every time.
Evaluate before you buy
Assess vendors against security, privacy, data-retention and compliance criteria before anyone signs up.
Set boundaries first
Configure permissions, labels and data-loss controls so AI only reaches what it should.
Launch with confidence
Train people on safe use, monitor adoption and refine policy as usage grows.
We practise what we advise
Clients trust us with sensitive information. Our own use of AI follows the same standard we set for them.
- Client data is never used to train AI models
- Privacy-first tooling, with local processing where required
- Internal AI use governed by our own published policy
- Tools chosen for each use case, never one-size-fits-all
What is shadow AI?
Shadow AI is any AI tool, feature or agent used in your organisation without formal approval or oversight, from free chat assistants on personal accounts to AI features quietly switched on inside existing SaaS apps.
Can we engage you for AI governance without managed services?
Yes. Our advisory services stand alone. Many clients start with an assessment or governance framework and add managed controls later if they need them.
Is Microsoft Copilot safe to use with sensitive data?
It can be, once permissions, sensitivity labels and data-loss controls are in place. Copilot respects existing access rights, so the real risk is historic oversharing. We fix that before rollout.
How does the EU AI Act affect us?
If you build, deploy or distribute AI systems in the EU, you likely have obligations that are phasing in over the next few years. We help you classify your AI systems by risk level and put proportionate controls in place.
Do you help with ISO/IEC 42001 certification?
Yes. We run gap analyses, build the AI management system, prepare evidence and support you through the certification audit.
How quickly can we get started?
An initial consultation can usually be arranged within days. Assessments are fixed in scope so you know exactly what you'll receive and when.
Talk to an AI security consultant
A 20-minute conversation to understand where you are on your AI journey and what to do next.